> ## Documentation Index
> Fetch the complete documentation index at: https://moengage.com/docs/llms.txt
> Use this file to discover all available pages before exploring further.
# Web オプトインの取得が Content Security Policy ディレクティブに違反するのはなぜですか?
> CSP の img-src ディレクティブで必要な MoEngage の画像 URL をホワイトリストに登録し、Web プッシュのオプトインをブロックする Content Security Policy エラーを修正します。
## 問題
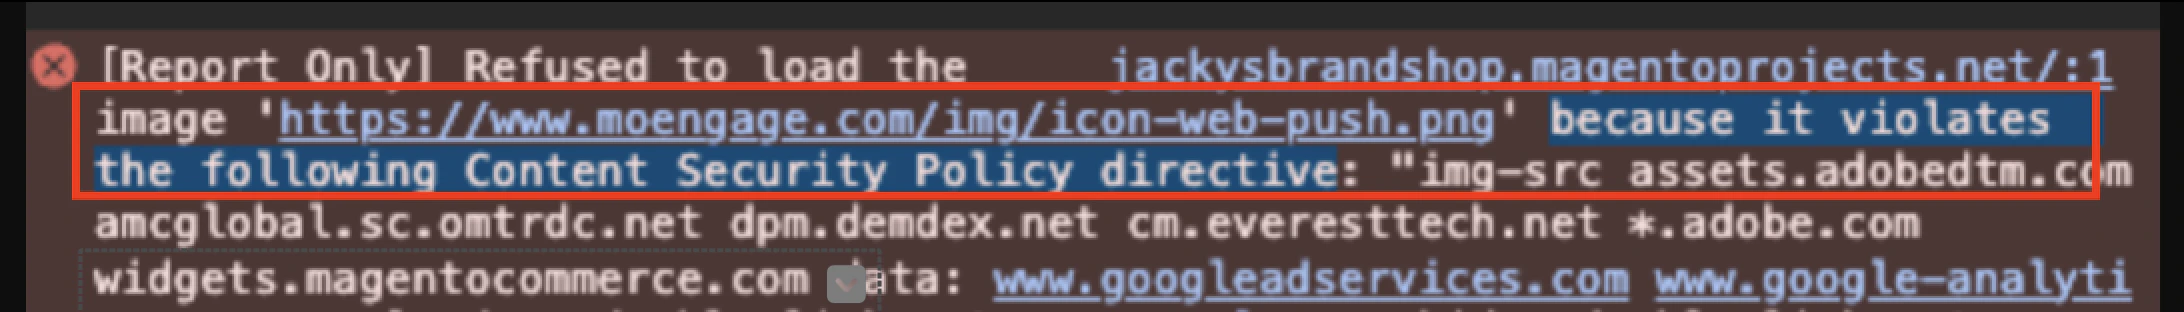
ユーザーが Web オプトインを取得しようとすると、ブラウザのコンソールに次のエラーメッセージが表示されます。
"[https://www.moengage.com/img/icon-web-push.png](https://www.moengage.com/img/icon-web-push.png) because it violates the following Content Security Policy directive: "img-src assets.adobedtm.com amcglobal.sc.omtrdc.net".
 ## 解決策
次の手順を実行してください。
この問題は、Web オプトイン用にアップロードされた画像アイコンで発生します。
1. アップロードされた画像に必要なアクセス権があることを確認します。
2. 顧客側の Content Security Policy (CSP) の image-src ディレクティブで、URL `` をホワイトリストに登録します。詳細については、[Whitelisting URLs](/docs/ja/developer-guide/web-sdk/web-sdk-integration/basic-integration/web-sdk-integration) を参照してください。